> ## Documentation Index
> Fetch the complete documentation index at: https://docs.guardhousehq.com/llms.txt
> Use this file to discover all available pages before exploring further.

# Set up SSO with SAML

> Let your staff sign in to Guardhouse with their Microsoft accounts using a SAML enterprise application in Microsoft Entra ID.

Single sign-on (SSO) lets your users sign in to Guardhouse with their existing Microsoft work accounts.
You set it up by creating a SAML enterprise application in Microsoft Entra ID (formerly Azure Active Directory)
and exchanging a few configuration values with Guardhouse.

## Before you begin

Setting up SSO is a joint process between you and Guardhouse.

### What Guardhouse provides

Guardhouse supplies the values you need for the SAML configuration:

* **Identifier (Entity ID)**
* **Reply URL (Assertion Consumer Service URL)**
* **Sign-on URL**
* **Logout URL**

### What you provide to Guardhouse

Send Guardhouse the following details:

* **Your Microsoft tenant ID.** In the Azure portal, search for **Tenant ID** within Microsoft Entra ID.

* **Your preferred company name.** Guardhouse uses this in the custom sign-on URL for your application.
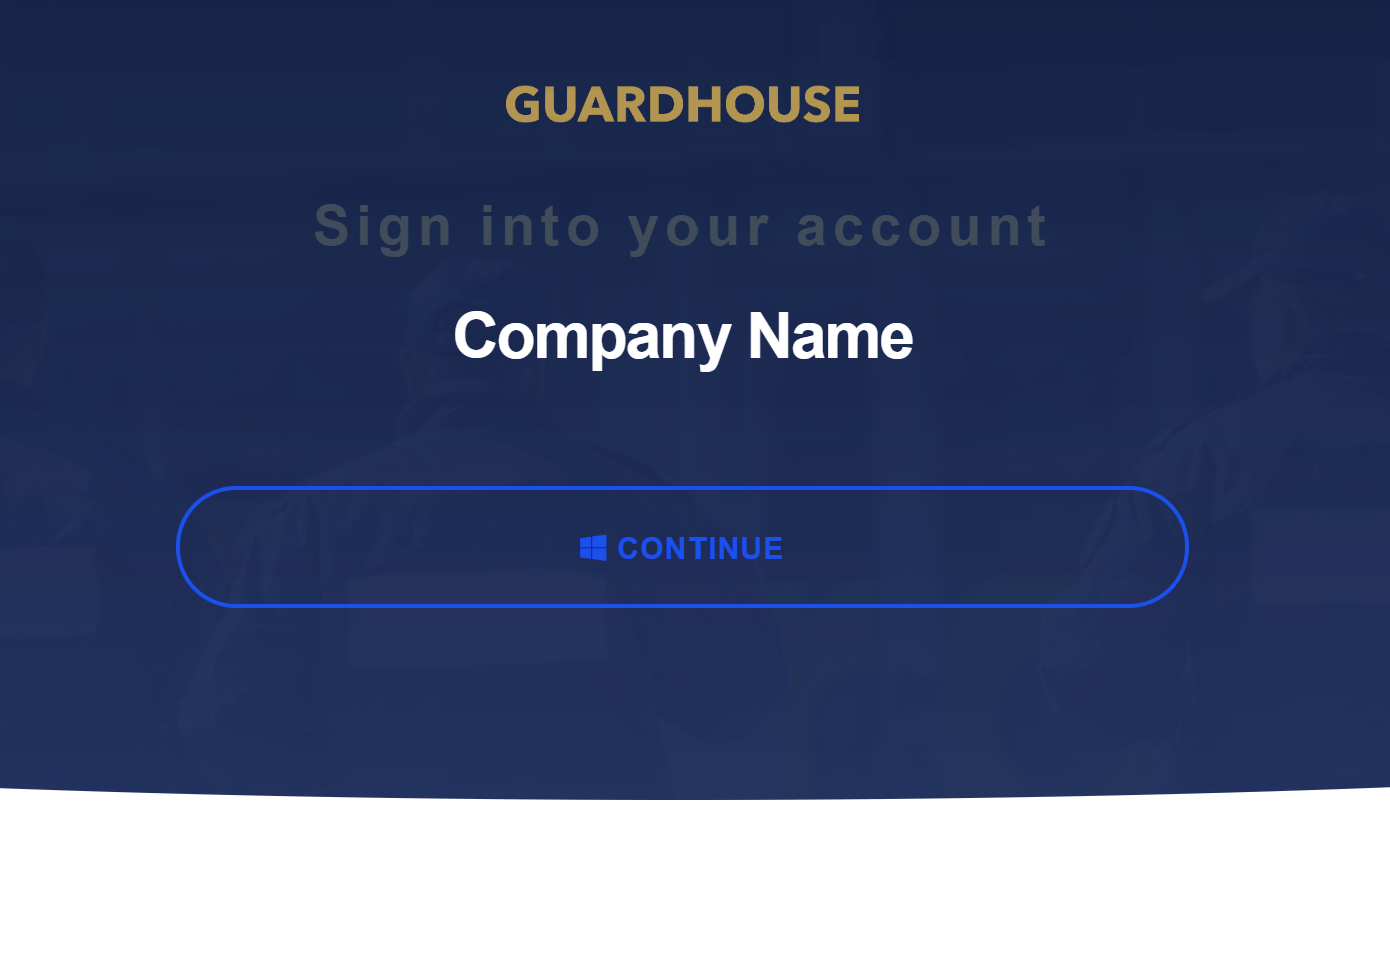
  <Frame caption="The company name appears on your custom Guardhouse sign-in page.">
    <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/login-company-name.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=5c9c9eae7483070992670f0a2fc19bb7" alt="Guardhouse sign-in page showing a company name above a Continue button with the Microsoft logo" width="1390" height="968" data-path="images/guides/sso-saml/login-company-name.png" />
  </Frame>

* **Your preferred domain.** This is the domain your users enter when they sign in to Guardhouse.
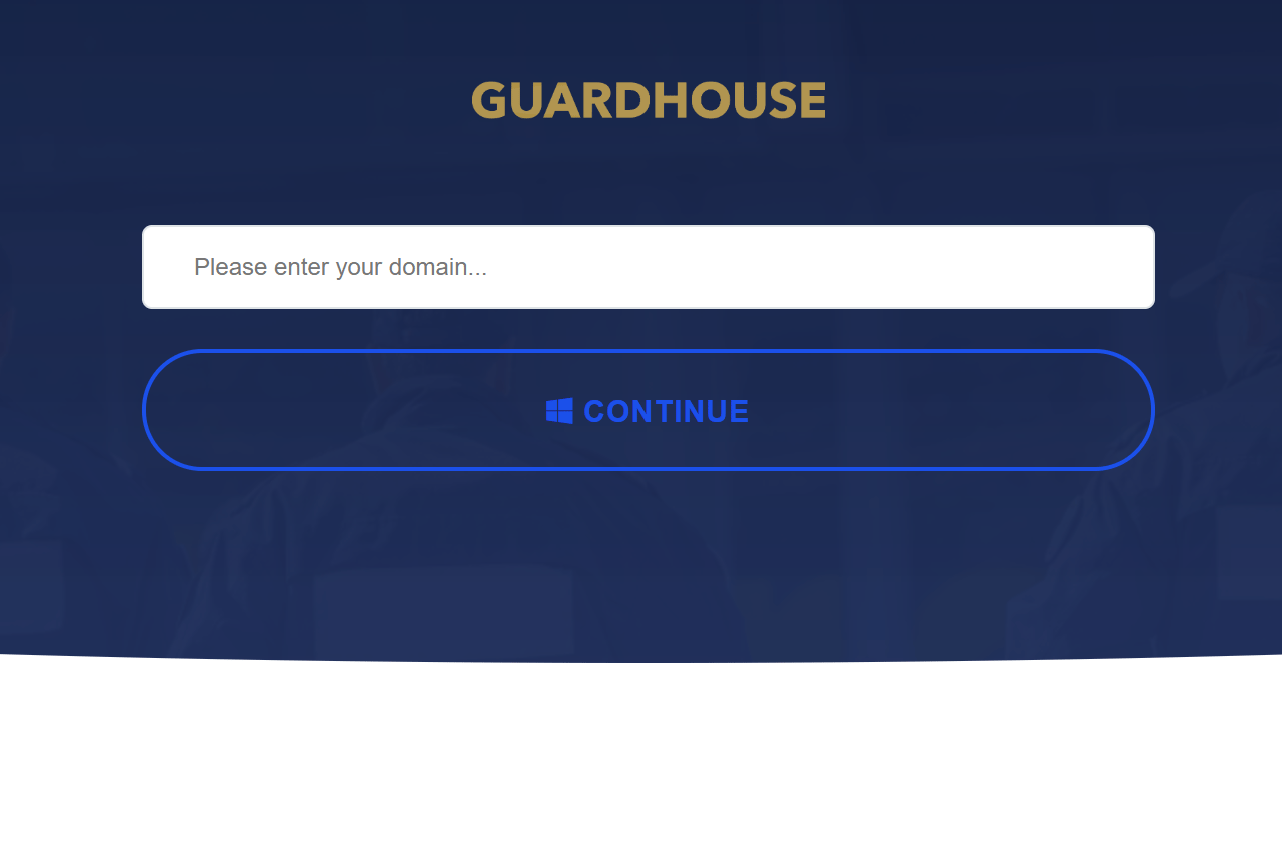
  <Frame caption="Users enter your domain on the Guardhouse sign-in page.">
    <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/login-domain.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=6c7c16472f66fcf2e81cb43155d4121e" alt="Guardhouse sign-in page with a domain input field and a Continue button" width="1282" height="846" data-path="images/guides/sso-saml/login-domain.png" />
  </Frame>

* **Your security groups and their company entities (multiple-company setups only).** Provide a list of your
  Azure security groups and the Guardhouse company entity each one maps to.
  See [Multiple-company setup](#multiple-company-setup).

## Step 1: Create an enterprise application

1. Sign in to the [Azure portal](https://portal.azure.com) with an administrator account.

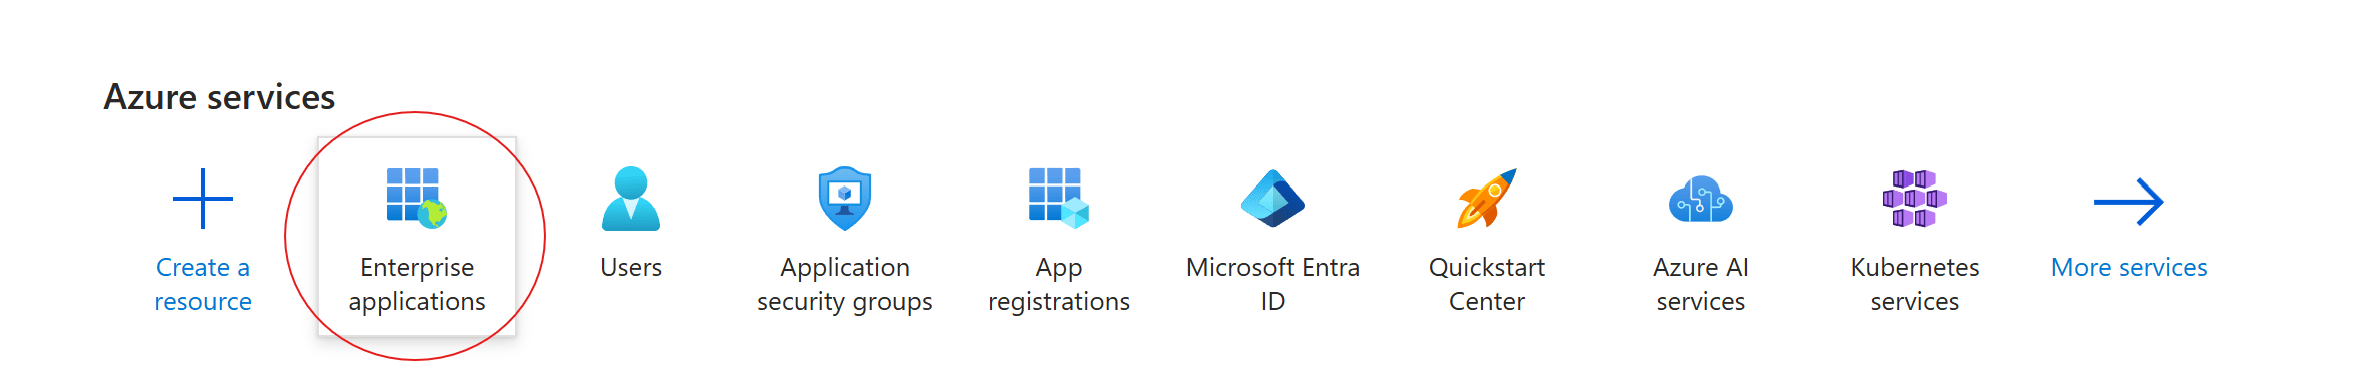
2. Under **Azure services**, select **Enterprise applications**.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/azure-enterprise-applications.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=d6f94b7a41cbaaee3088d58baba14762" alt="Azure services list with Enterprise applications highlighted" width="2380" height="370" data-path="images/guides/sso-saml/azure-enterprise-applications.png" />
   </Frame>

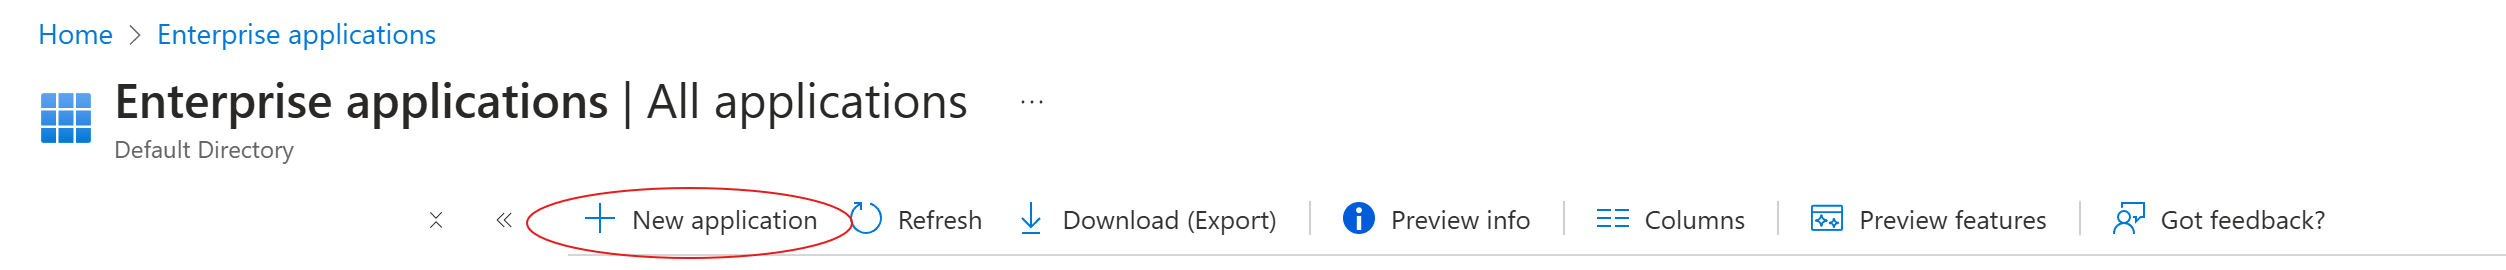
3. Click **New application**.

   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/new-application.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=ca78ac39bd01cf38e76c452c5be9fe2b" alt="Enterprise applications page with New application highlighted in the toolbar" width="2506" height="270" data-path="images/guides/sso-saml/new-application.png" />
   </Frame>

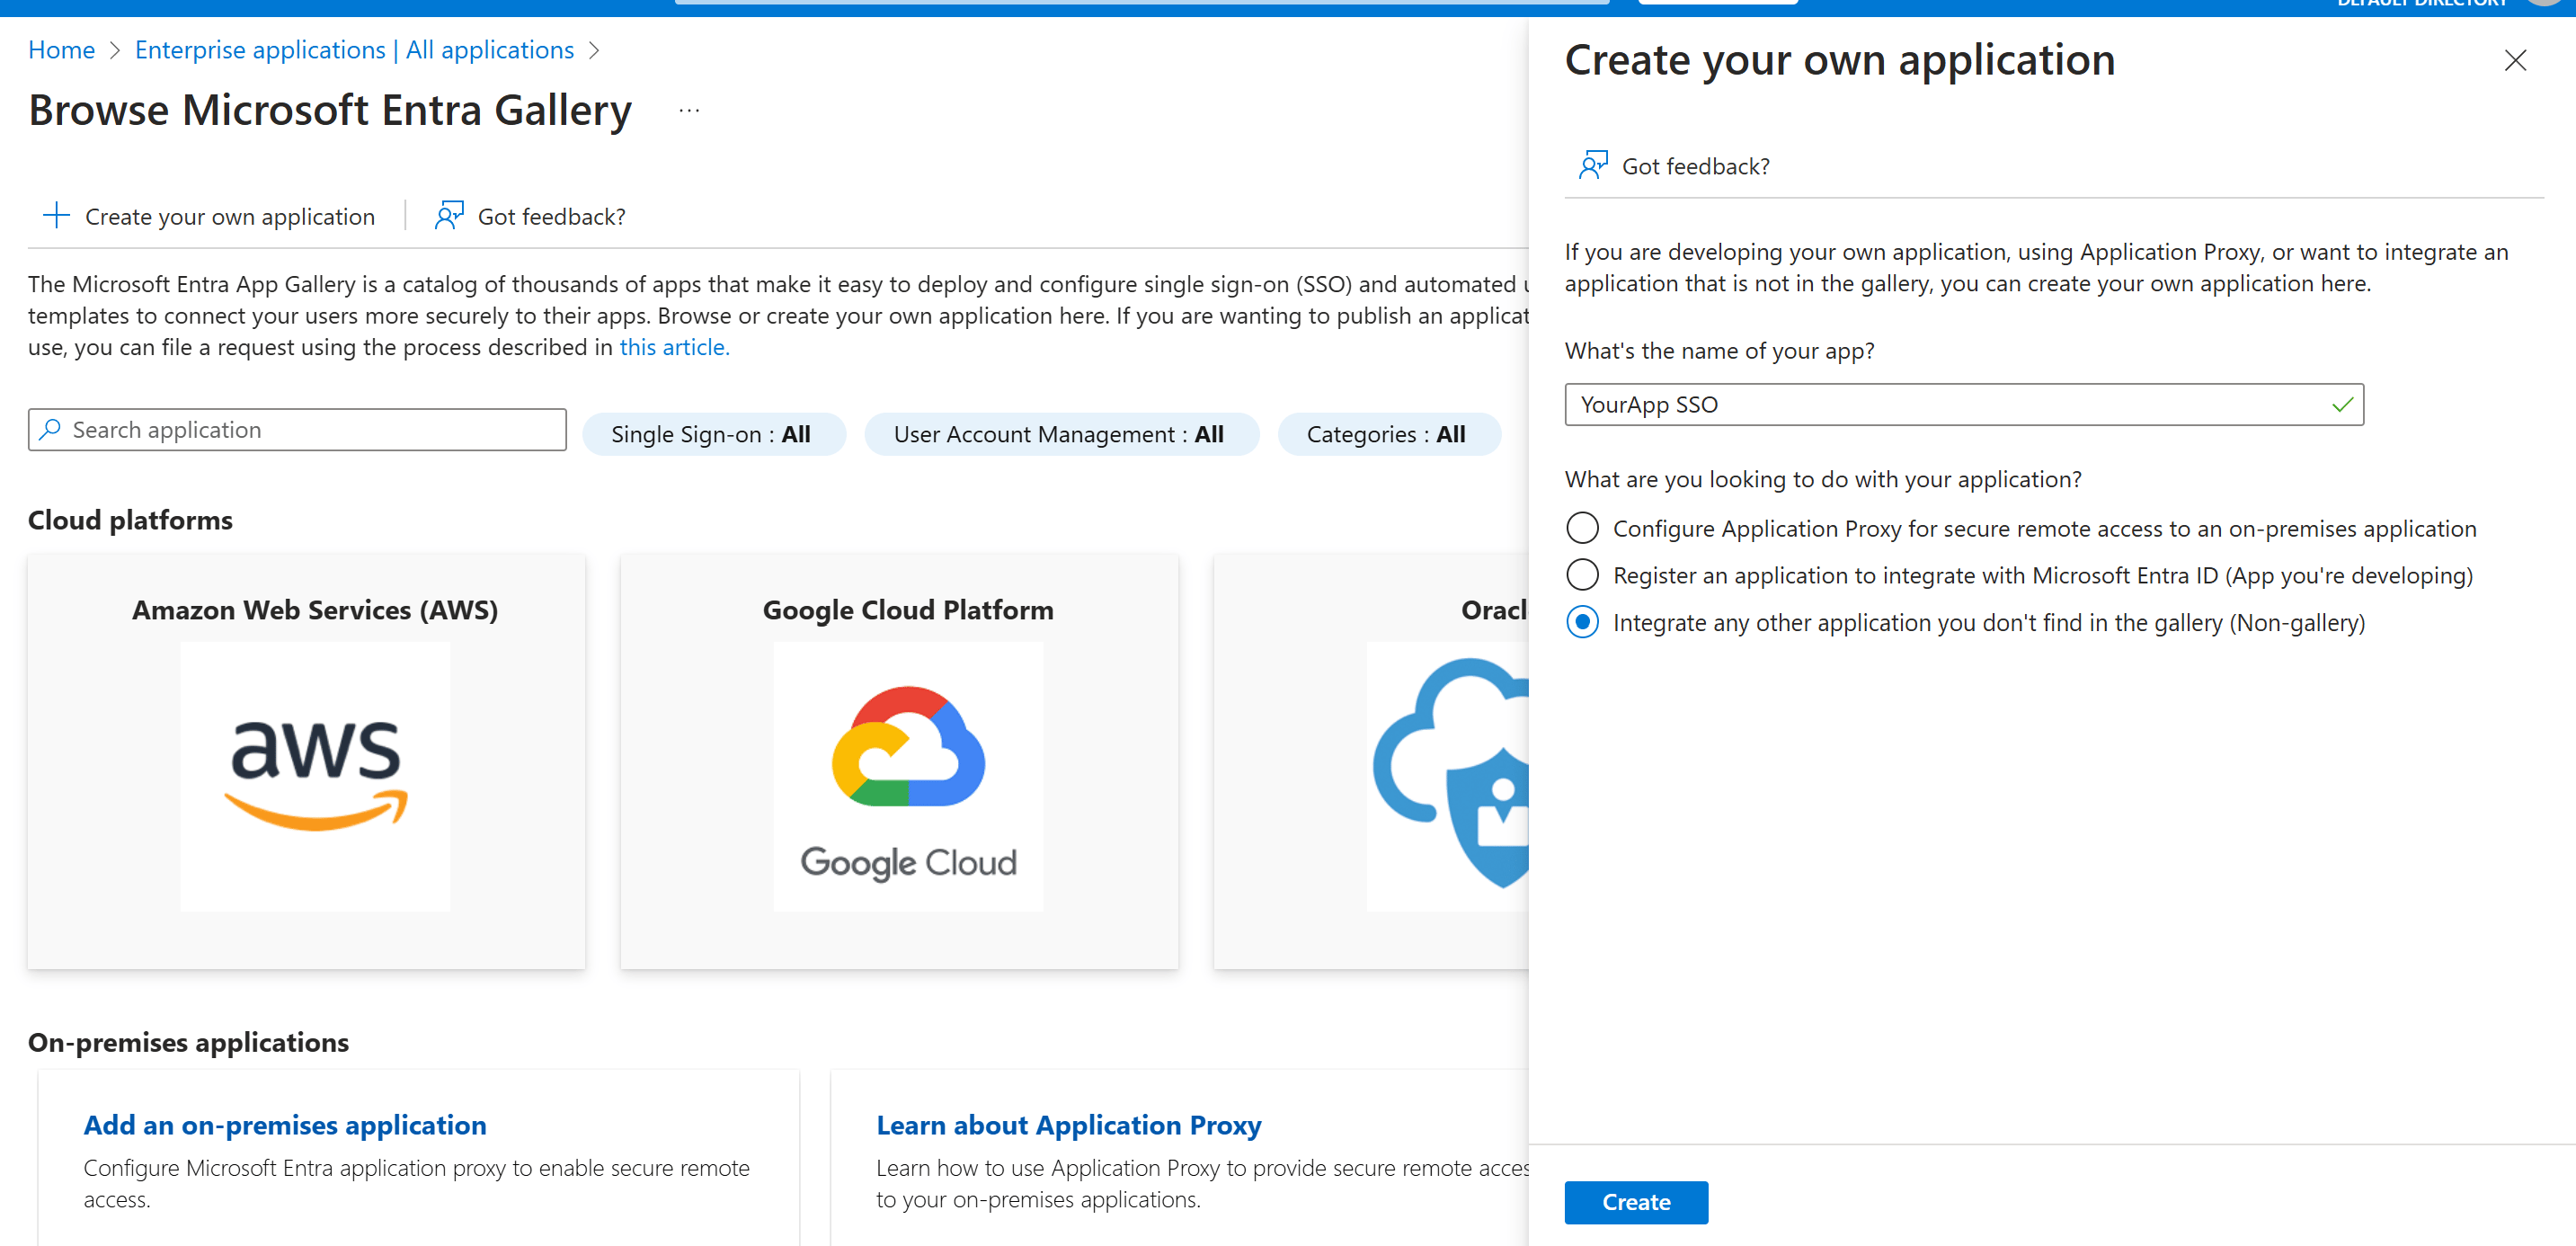
4. Click **Create your own application**.

5. Enter a name for the application, for example `YourApp SSO`.

6. Select **Integrate any other application you don't find in the gallery (Non-gallery)**.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/create-your-own-application.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=027869a86a9f57b6c6f95ec7e68ee762" alt="Create your own application panel with an app name entered and the Non-gallery option selected" width="2866" height="1386" data-path="images/guides/sso-saml/create-your-own-application.png" />
   </Frame>

7. Click **Create**.

## Step 2: Configure SAML single sign-on

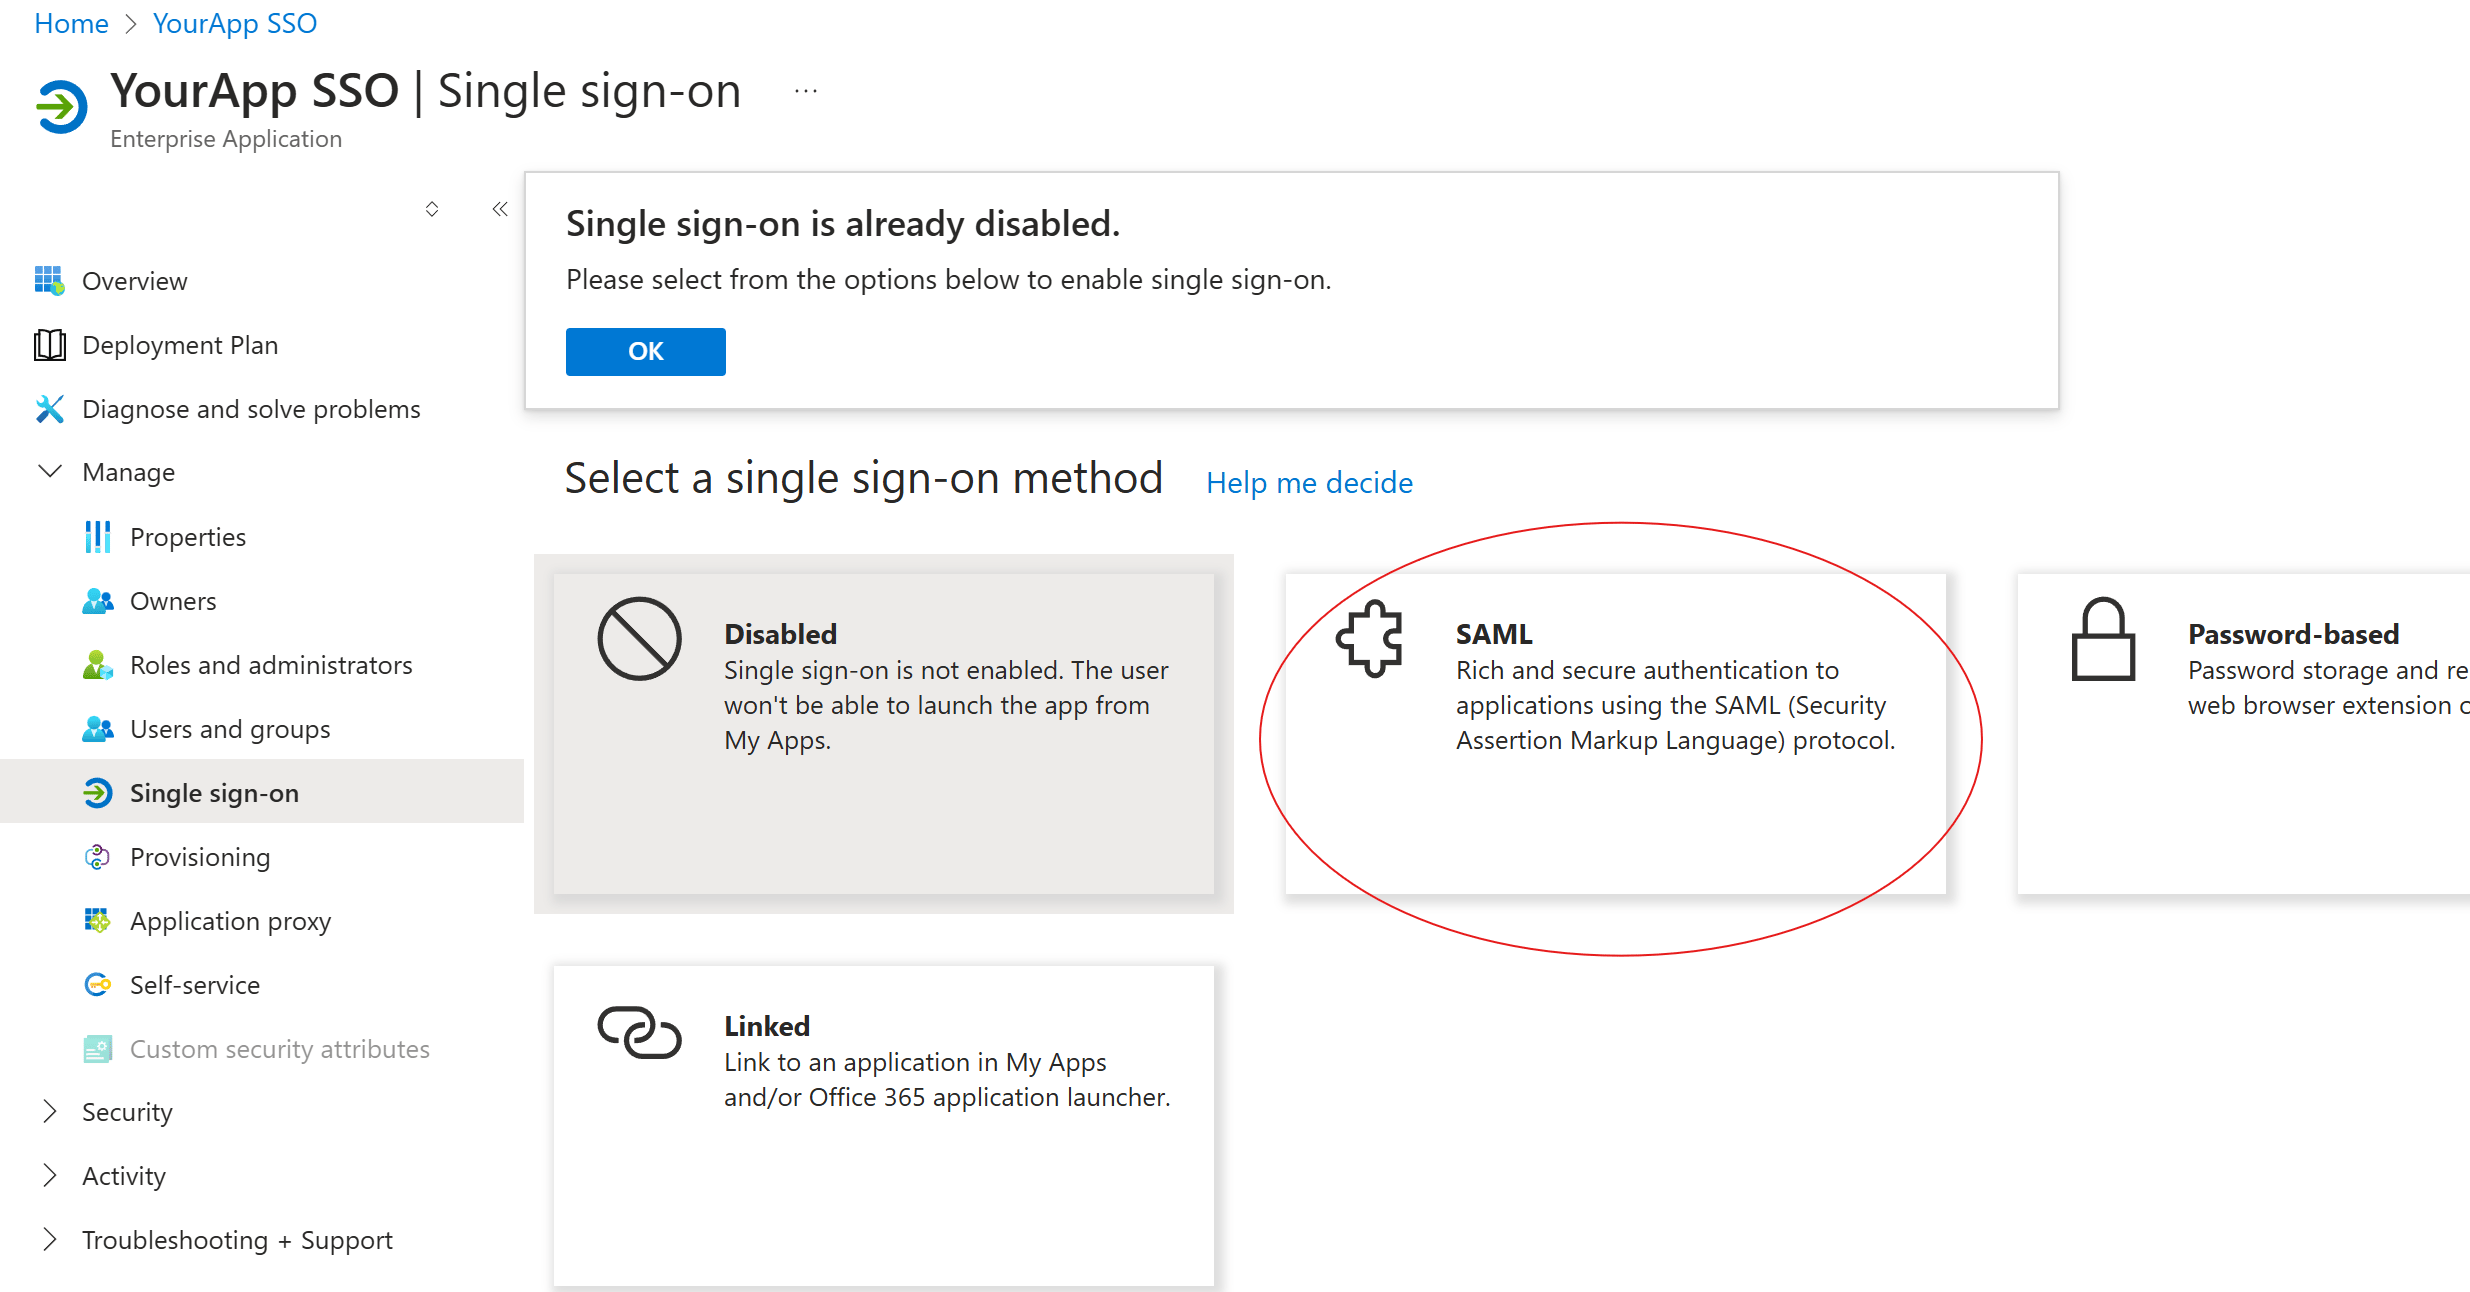
1. In your new application, select **Single sign-on**.

2. Select **SAML** as the single sign-on method.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/select-saml.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=e7102730141c3dd571a0b46c391ec979" alt="Select a single sign-on method page with the SAML option highlighted" width="2470" height="1292" data-path="images/guides/sso-saml/select-saml.png" />
   </Frame>

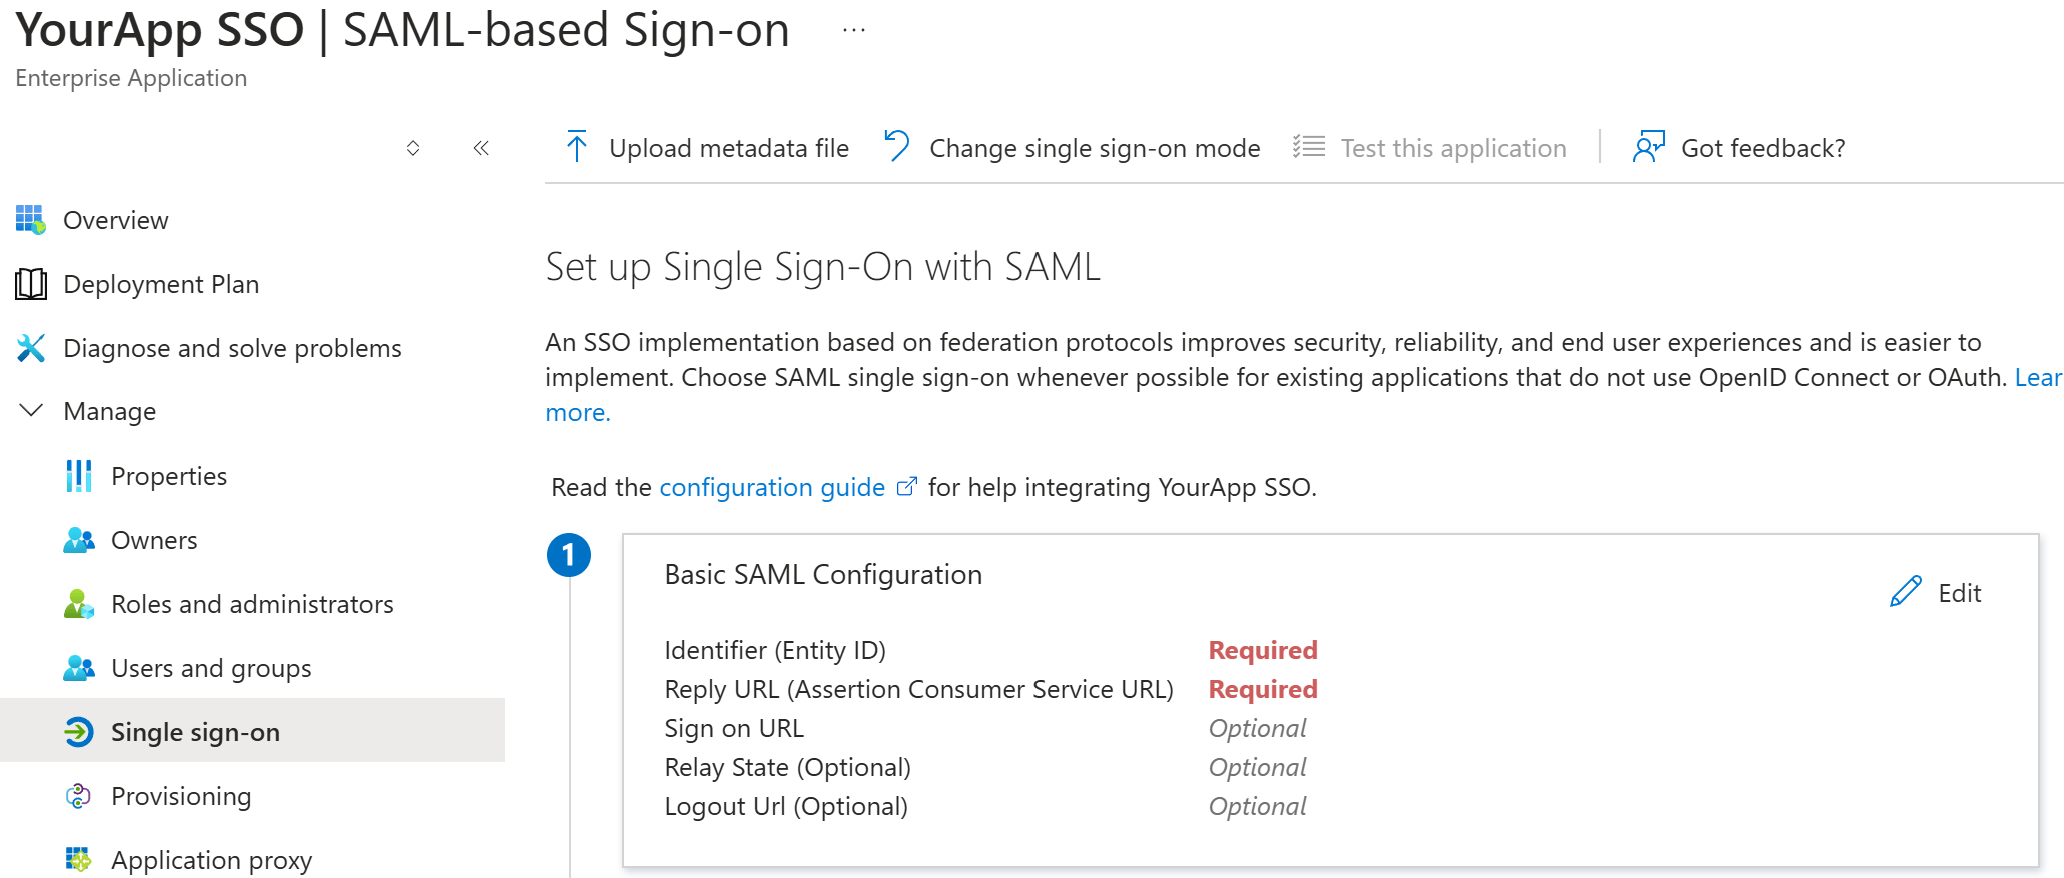
3. In the **Basic SAML Configuration** section, click **Edit**.

4. Enter the values that Guardhouse provided:

   * **Identifier (Entity ID)**: the unique identifier for your application.
   * **Reply URL (Assertion Consumer Service URL)**: the endpoint that receives SAML assertions from Microsoft Entra ID.
   * **Sign on URL**: the direct sign-in URL for your application.
   * **Logout Url**: the endpoint users are redirected to after they sign out.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/basic-saml-configuration.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=599b7f8f6a0e4dd6912b5b317b0283ff" alt="SAML-based Sign-on page showing the Basic SAML Configuration section with Identifier, Reply URL, Sign on URL, Relay State, and Logout URL fields" width="2064" height="878" data-path="images/guides/sso-saml/basic-saml-configuration.png" />
   </Frame>

5. Click **Save**.

<Note>
  Leave the other sections on the SAML-based Sign-on page (**Attributes & Claims**, **SAML Certificates**,
  and **Set up**) at their default settings. For a multiple-company setup, you add a group claim to
  **Attributes & Claims** in [Step 3](#multiple-company-setup).
</Note>

## Step 3: Assign users and groups

Choose the setup that matches your organization:

* **Single-company setup**: all your users belong to one Guardhouse company.
* **Multiple-company setup**: your users belong to different Guardhouse company entities, and Guardhouse
  uses Azure security groups to map each user to the right one.

### Single-company setup

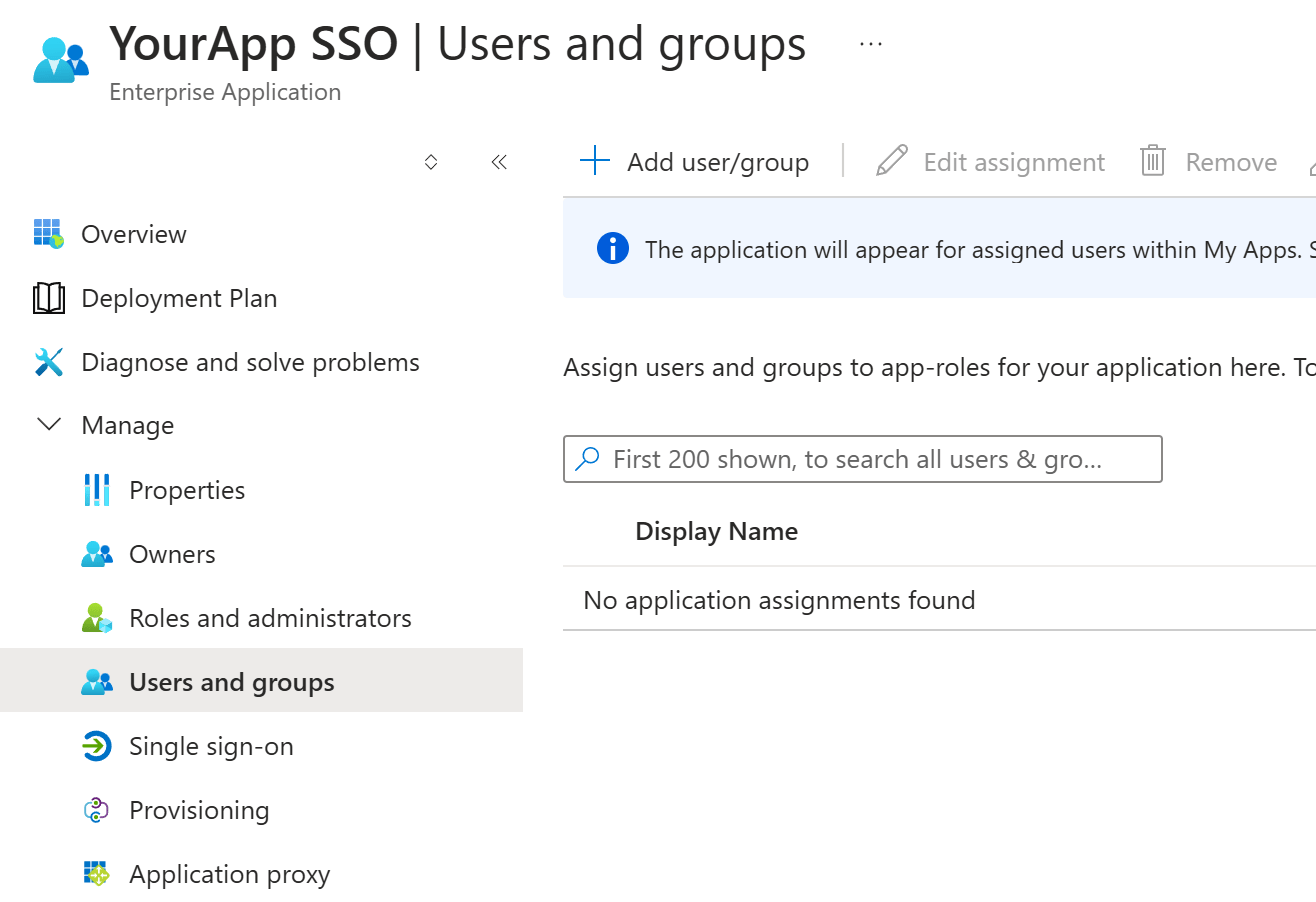
1. In the Azure portal, open your enterprise application.

2. Select **Users and groups**.

3. Click **Add user/group**.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/users-and-groups.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=23413c0d7b1d743ec17e172a6dc942b2" alt="Users and groups page for the enterprise application with Add user/group in the toolbar" width="1316" height="902" data-path="images/guides/sso-saml/users-and-groups.png" />
   </Frame>

4. Select the users or groups that should have access to Guardhouse.

5. Optionally, assign a role if your application uses role-based access.

6. Review your selections, then click **Assign**.

<Warning>
  Assign only authorized users and groups to the application. Anyone you assign can sign in to Guardhouse.
</Warning>

### Multiple-company setup

#### Create security groups

1. Create a security group for each company, either in Azure or on-premises.
2. Add the user accounts to their respective groups.
3. Send Guardhouse the list of groups so they can map each one to the correct company entity.

For example:

| Your Azure security group | Your company entity in Guardhouse |
| - | - |
| `Security_Group_1` | Company A |
| `Security_Group_2` | Company B |
| `Security_Group_3` | Company C |

#### Assign the groups to the application

1. In the Azure portal, open your enterprise application.

2. Select **Users and groups**.

3. Click **Add user/group**.

   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/users-and-groups.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=23413c0d7b1d743ec17e172a6dc942b2" alt="Users and groups page for the enterprise application with Add user/group in the toolbar" width="1316" height="902" data-path="images/guides/sso-saml/users-and-groups.png" />
   </Frame>

4. Select the security groups you created.

5. Optionally, assign a role if your application uses role-based access.

6. Review your selections, then click **Assign**.

<Warning>
  Assign only authorized users and groups to the application. Anyone you assign can sign in to Guardhouse.
</Warning>

#### Add a group claim

The group claim tells Guardhouse which security groups a user belongs to.

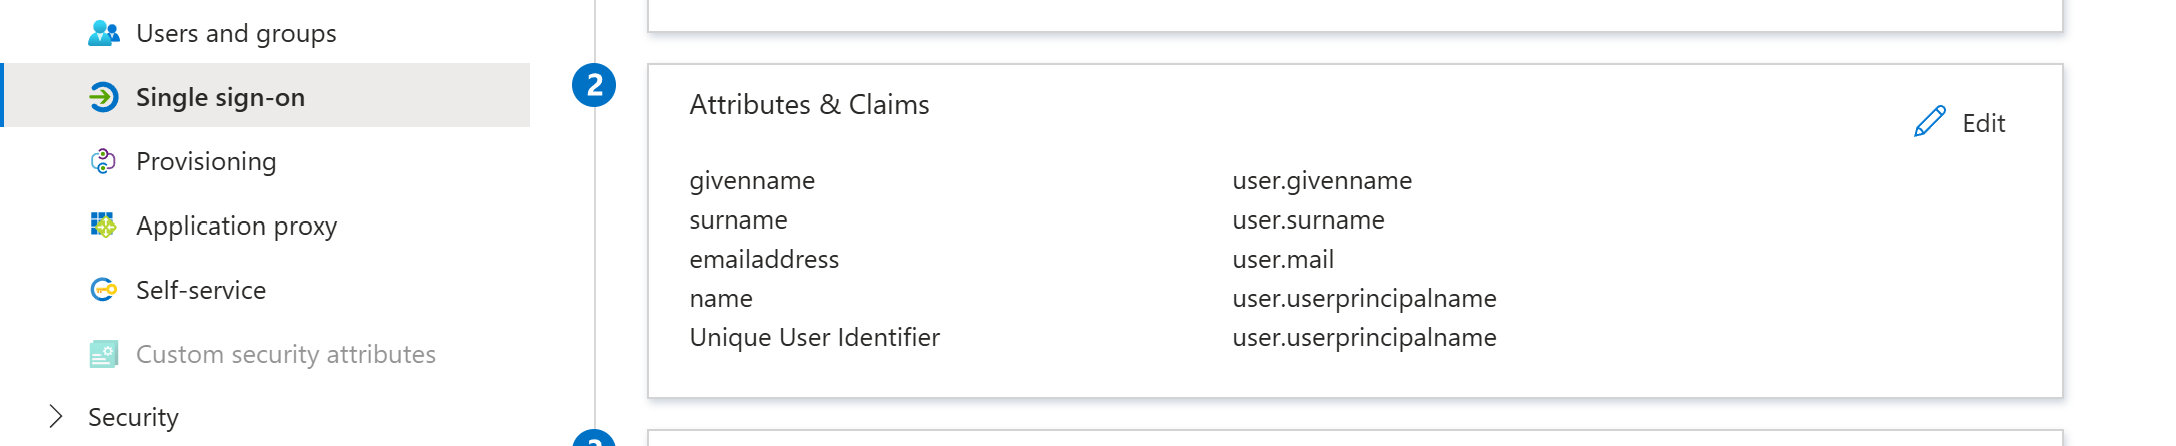
1. Select **Single sign-on**, then click **Edit** in the **Attributes & Claims** section.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/attributes-and-claims-edit.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=dcdc1d133423580ba5a546c7cf0f9c17" alt="Attributes & Claims section on the SAML-based Sign-on page with the Edit button" width="2176" height="446" data-path="images/guides/sso-saml/attributes-and-claims-edit.png" />
   </Frame>

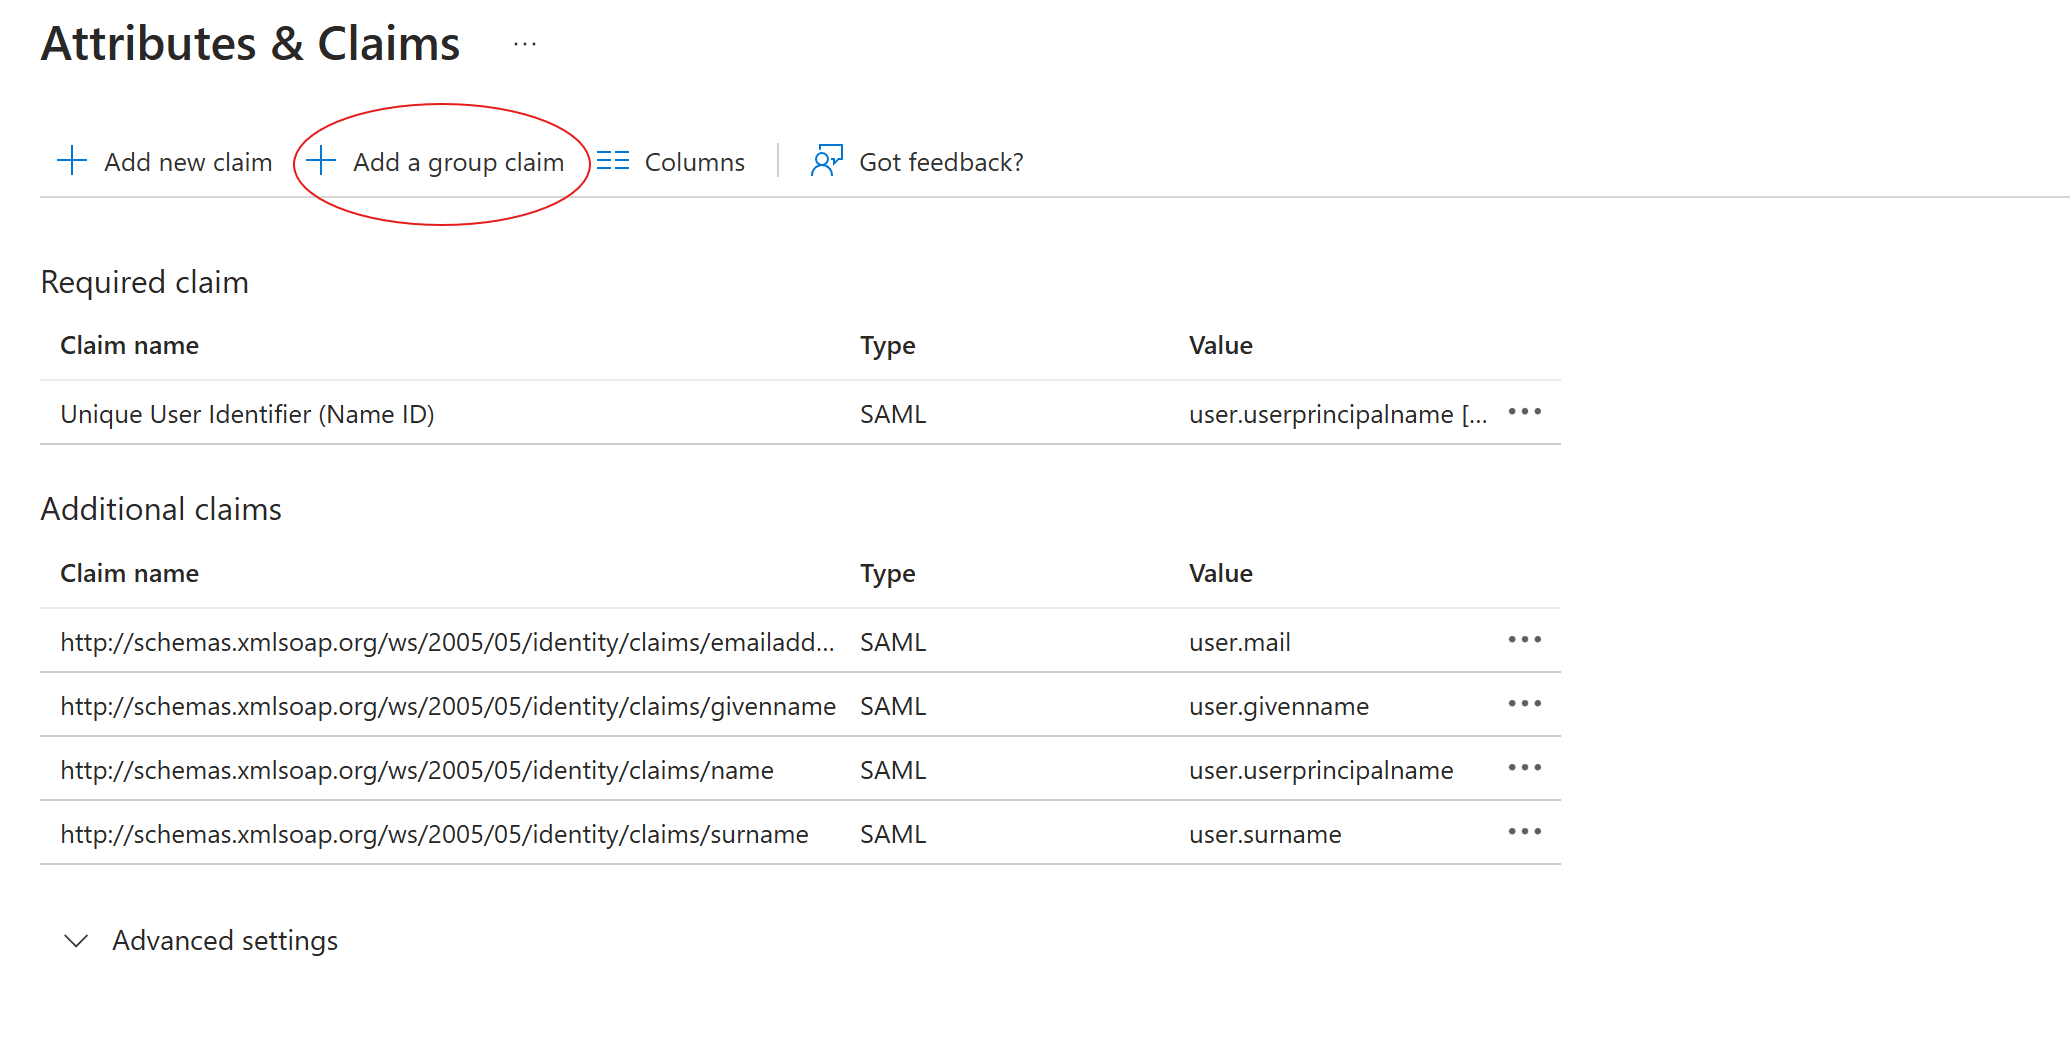
2. Click **Add a group claim**.

   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/add-group-claim.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=59134b8a639c7443e6407757f2ae50ef" alt="Attributes & Claims page with Add a group claim highlighted" width="2070" height="1040" data-path="images/guides/sso-saml/add-group-claim.png" />
   </Frame>

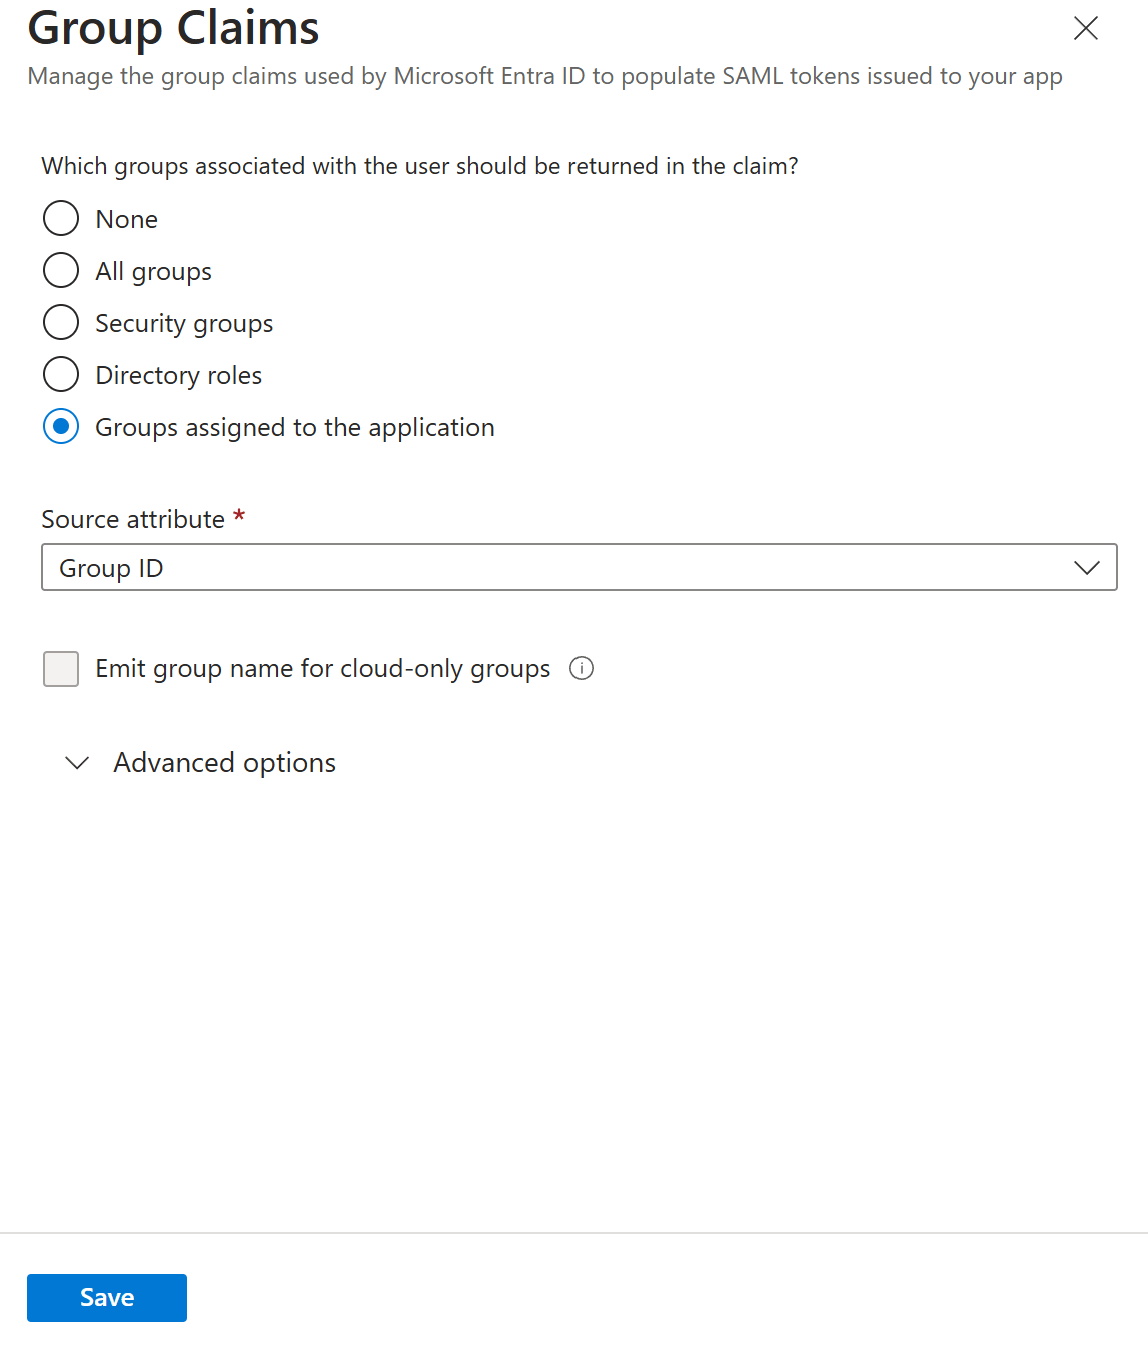
3. Under **Which groups associated with the user should be returned in the claim?**, select
   **Groups assigned to the application**.

4. Click **Save**.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/group-claims-panel.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=ff967ea259a87c6bdbb62704ce21ee9b" alt="Group Claims panel with Groups assigned to the application selected and Source attribute set to Group ID" width="1148" height="1348" data-path="images/guides/sso-saml/group-claims-panel.png" />
   </Frame>

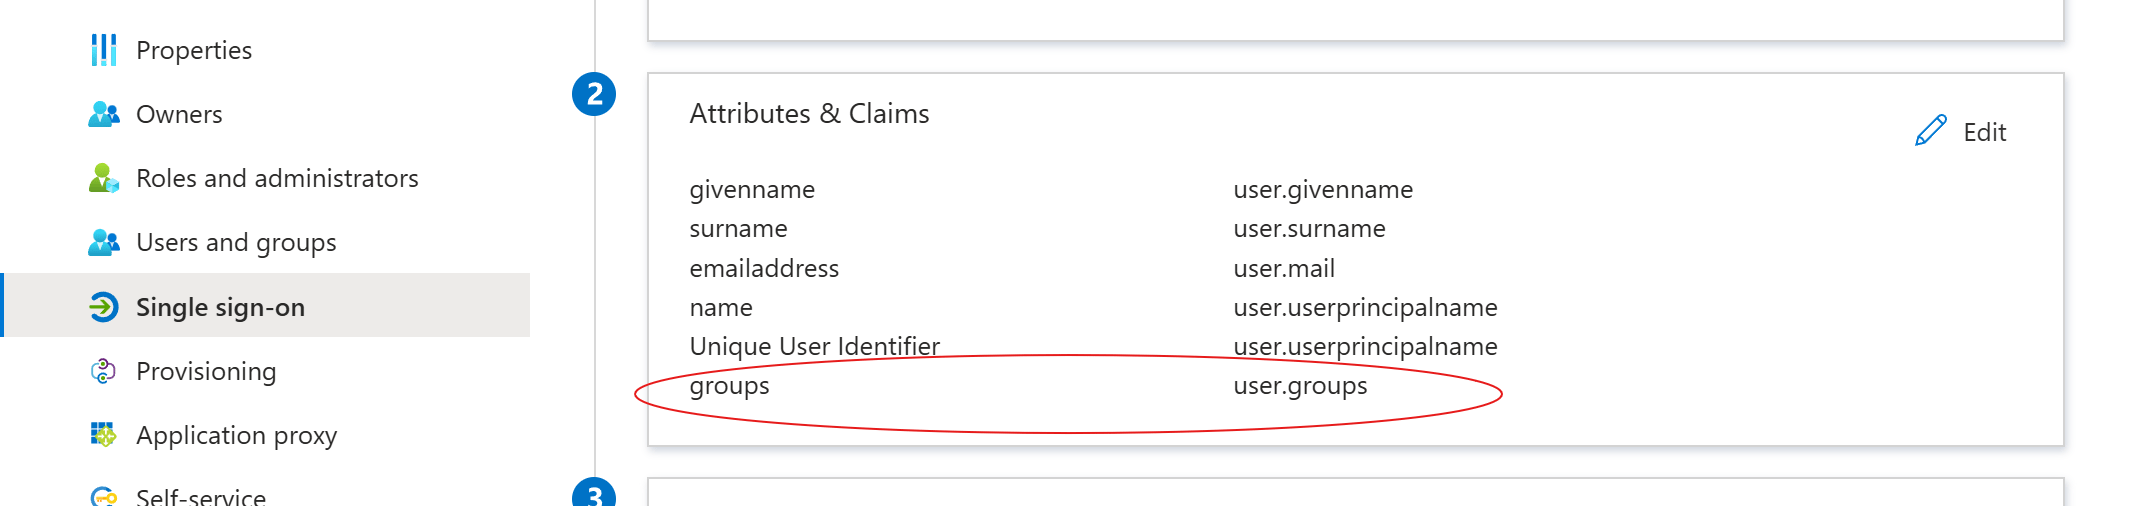
5. Confirm that a `groups` claim now appears in the list.

   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/group-claim-added.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=38166cb2db269d87ecf5d4bf1f18f2fb" alt="Attributes & Claims page listing the new groups claim with the value user.groups [ApplicationGroup]" width="1661" height="1066" data-path="images/guides/sso-saml/group-claim-added.png" />
   </Frame>

   The claim also appears in the **Attributes & Claims** summary on the SAML-based Sign-on page.
   <Frame>
     <img src="https://mintcdn.com/guardhouse/tuwl4ruFPg44mn-F/images/guides/sso-saml/attributes-and-claims-groups.png?fit=max&auto=format&n=tuwl4ruFPg44mn-F&q=85&s=072ef793f267684b615c5340ee519033" alt="Attributes & Claims summary showing groups mapped to user.groups" width="2136" height="506" data-path="images/guides/sso-saml/attributes-and-claims-groups.png" />
   </Frame>